Technology
Custody, keys and the trust stack
Institutional custody depends on an aligned system of legal rights, operational controls and recovery procedures, not key security alone.
Monday, 28 September 2026 · 09:00 UTC (demo) · 4 min read · 966 words
 Democratize
A key is not a title deed
Digital asset custody is often introduced as a problem of protecting private keys. That is a necessary starting point, but an inadequate conclusion. A key can authorise an action on a network without establishing who is legally entitled to the asset, who may instruct the holder of the key or what happens if a transaction is disputed. For institutional investors, custody is a relationship between technical control and enforceable rights. Both sides need to be understood.
The distinction is especially important for tokenised real assets. A token may represent an interest recorded through a company, trust, fund or contractual arrangement. The legal significance of holding it depends on that structure and its governing documents. If the token record and another ownership register diverge, investors need to know which is authoritative and how the inconsistency is resolved. Secure possession of a credential does not answer that question.
A useful custody assessment therefore begins with the claim rather than the wallet. What exactly is being held? For whose benefit? Under which law? Which records establish entitlement? Only then does it become possible to judge whether the technical arrangements preserve the intended relationship. The strongest security architecture cannot repair an uncertain claim, just as clear documents cannot compensate for controls that permit unauthorised transfers.
Separate the layers of trust
The trust stack includes more than a custodian. It may involve the issuer, an administrator, a technology provider, identity services and the operators of the underlying network. Each performs a different function, and some may rely on others. Mapping these dependencies is more useful than assigning the whole arrangement a single label such as institutional grade. The assessment should identify who can act, who can fail and whose records matter when accounts disagree.
Asset segregation requires the same precision. Operational separation of accounts is not necessarily equivalent to legal segregation in insolvency. Investors should understand the basis on which assets are held, the nature of their claim against the custodian and any involvement of subcustodians. A pooled technical address may support separately recorded entitlements, but those records and the associated legal arrangements need to be robust. Conversely, a dedicated address is not by itself proof of insolvency protection.
Key management remains essential within this wider framework. Controls may distribute signing authority, restrict destinations or require several approvals. Their value depends on implementation and governance, not vocabulary. An institution needs to understand how transactions are authorised, how policies are changed and whether a person with administrative access can bypass ordinary controls. Security should be assessed across the full instruction process, including the systems through which authorised staff submit requests.
Custody is the ability to preserve and exercise a legal entitlement through ordinary operations, human error and institutional failure.
Recovery is part of security
An arrangement that prevents theft but cannot recover from a lost credential has solved only part of the problem. Staff leave, devices fail and authority changes. Family offices face succession questions; investment managers face personnel changes and mandate transitions. Recovery procedures must preserve continuity without creating an easy alternative route for an attacker. That requires a clear standard of evidence, defined approval powers and a record of every exceptional intervention.
Tokenised instruments may allow an authorised party to freeze a holding, replace a token or update a register. These powers can support lawful recovery, but they also create concentrations of control. Their existence should be disclosed rather than treated as an embarrassing deviation from technical purity. Investors need to know the circumstances in which powers can be used, the safeguards around them and the consequences for a holder who disputes the action.
Testing matters because a written recovery policy is not the same as a working recovery capability. The relevant exercise is broader than restoring a backup. It should consider how legal authority is established, how instructions reach the right parties and how records are reconciled afterwards. It should also consider whether a recovery action affects distributions, reporting or other holders. The objective is continuity of rights, not merely renewed access to an application.
Examine the difficult handovers
Custody arrangements should explain what happens when the service relationship ends. An investor may wish to appoint another provider, or a provider may cease supporting a network or instrument. A technically transferable token can still be difficult to move if the receiving custodian cannot support its restrictions or the issuer requires additional checks. Exit planning should address both the transfer of control and the migration of the records that make control intelligible.
Network changes introduce another form of handover. Upgrades, disruptions or competing transaction histories can require decisions about which system the instrument recognises. The governing framework should identify who makes those decisions and how holders are informed. Institutions should not have to infer legal consequences from a technology provider's operational announcement. Nor should they assume that every asset supported by a custodian follows the same rules simply because it appears in the same interface.
Insurance and audit can contribute evidence, but neither should be used as shorthand for complete protection. Coverage may have limits, exclusions and conditions; an assurance report addresses a defined scope. The useful inquiry is what each document actually establishes about the relevant service and period. Investors still need to understand residual exposure, including risks that sit outside the custodian's responsibility or depend on the issuer's own processes.
For Democratize, a pre-launch arranger, custody belongs within the design of the investment proposition rather than at its technical edge. Connecting real assets to institutional capital requires a credible account of ownership, delegated control and continuity. The aim is not to remove trust from the relationship. It is to make the location, limits and governance of that trust sufficiently clear to withstand scrutiny.
Information, not advice.
Marketplace connections
Related tokenisation themes, not recommendations. These fictional Blueprint assets are separate from the reported news; no publisher or source endorses them.
 Senior note: UK solar portfolioBig ticket · £120m illustrative asset valueTokenised SPV share register
 Bridging loan: Mayfair townhouse refurbishmentMedium ticket · £9.0m illustrative asset valueERC-3643 on a permissioned EVM chain
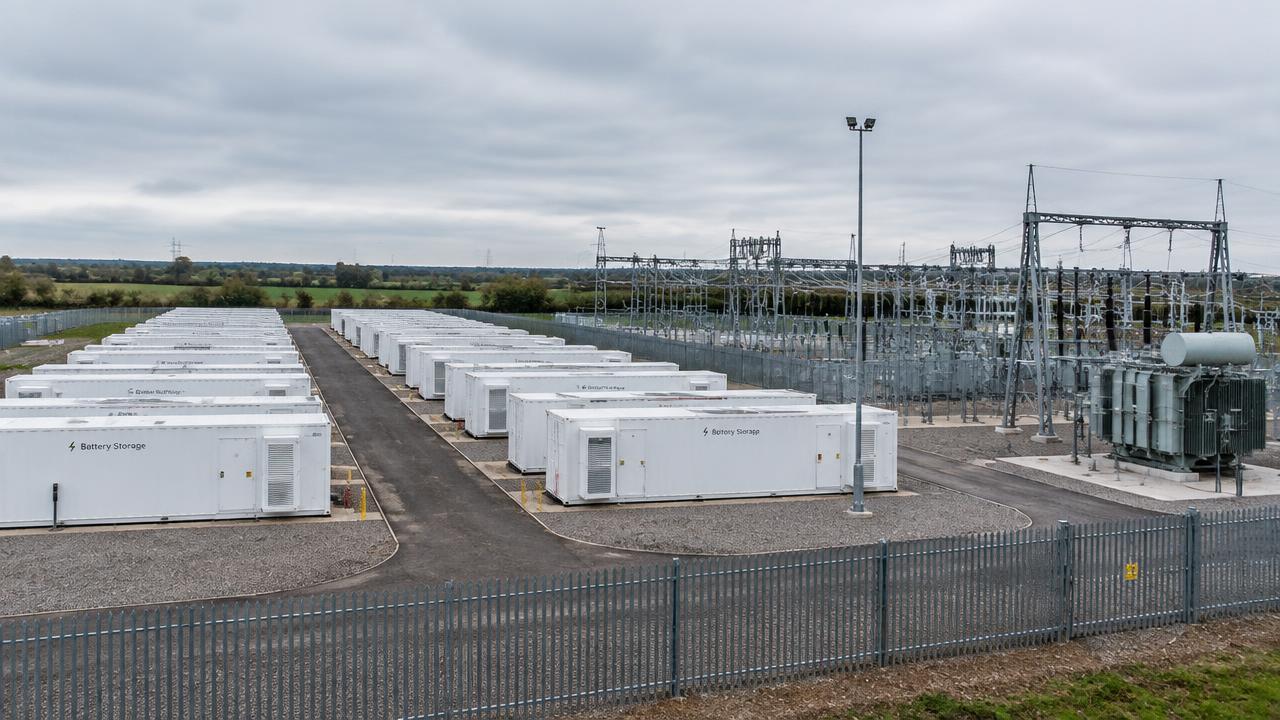 DLT bond: fictional community energy projectLow ticket · £750k illustrative asset valueDemonstration permissioned DLT bond register
Scale bands use whole fictional asset values: entry-level below £100k; low £100k–under £1m; medium £1m–under £10m; big £10m+. Not investment minimums or a statement of suitability. Blueprint: fictional data, not an offer, not live. Information, not advice.
Enjoyed this?
Get new Token+ Intel essays and the weekly tokenisation briefing every Monday.
Subscribe to the briefing
Token+ Intel desk
Claudia Harken
Head of Marketing and Communications
Claudia Harken leads marketing and communications at Democratize.